A reload of the module puts OPNsense's interfaces back, XGS 136, 2026-10-20
A reload of npuep.ko destroys every front port's interface and makes it again, and OPNsense is not
told. Until today the XGS 136 came back from one with its LAN bridge empty and without its address,
and the WAN on Port1 without its own - reachable over its console only, until three configctl calls
by hand. contrib/npuep/reload.sh now does what a boot does once the ports are back:
- the bridges made again with their members (
configctl interface bridge configure); - every interface assigned to a front port, a bridge, a VLAN, a LAGG or the management link to the
coprocessor configured again (
configctl interface reconfigure, one key at a time), and the rules; - the coprocessor's own end of the management link set again (
mgmt-link.sh coprocessor, as the bootup hook does) - its reset forgot it; - the PoE ports the owner switched off switched off again, and the cages' media told again.
- since the same evening, first of all, what a boot applies once the ports are there - the
coprocessor's acceleration gate, the never-offloaded list, the flow maker and the counts - from the
boot hook itself (
07-npuep settings). Without it a reload left the flow maker off whatever XGS: Settings said: found when an IPsec soak started after one reported "the flow maker off", and stopped; after a reload with it the flow maker, the counts to pf and to the ports read 1, and a reboot after the change came up with the same.
Script: images/deploy/lab-136-reload.sh, photographed; the series, lab-136-reload-series.sh, with
the console listened to beside it.
Measured
npuep.ko md5 db2f787a, reload.sh md5 f595caee:
| reloads with the put-back | 16 |
| the host lived through them | 15 |
| checked afterwards, each with the bridge's 10 members and its address, the WAN's DHCP address, the three static addresses and the management link back | 7 of 7 |
| a reload, start to the interfaces back | 80 seconds |
| stopped the host | 1 - the watchdog restarted it (603) |
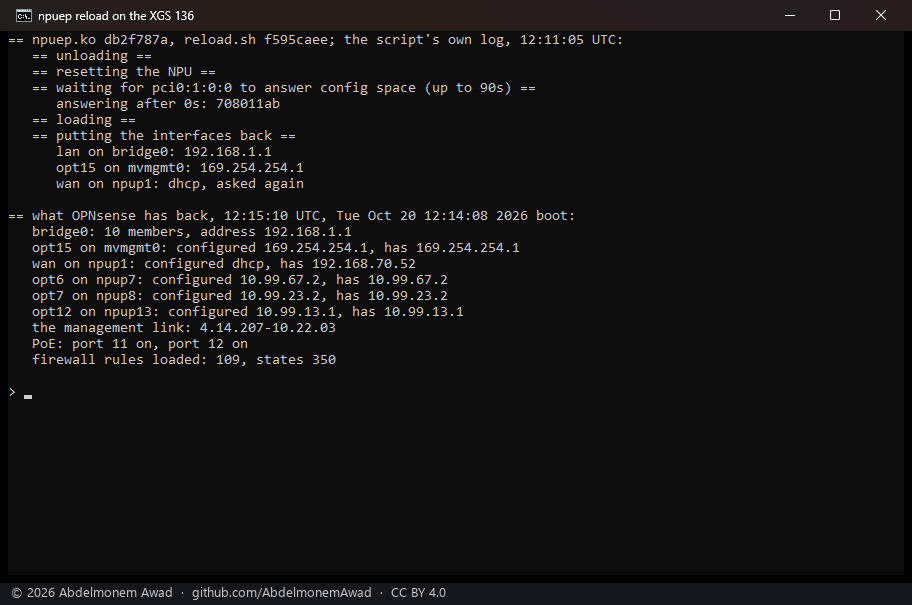
The first reload, before the script configured the management link again, came back with everything
but that: the coprocessor answered a ping and not ssh, until configctl interface reconfigure for the
management interface by hand.
What it does not mean
- One reload in sixteen stopped the host, with no message and no dump, while the interfaces were
being configured again and devd ran
rc.linkupfor the same ports; twelve more back to back did not. That stays open in 603. - Nothing in the product reloads the module. A boot loads it once; this is the developer's path.
The discussion of this page is held in the project's GitHub Discussions. Showing it here loads giscus from giscus.app and GitHub, and writing in it needs a GitHub account - what that means.